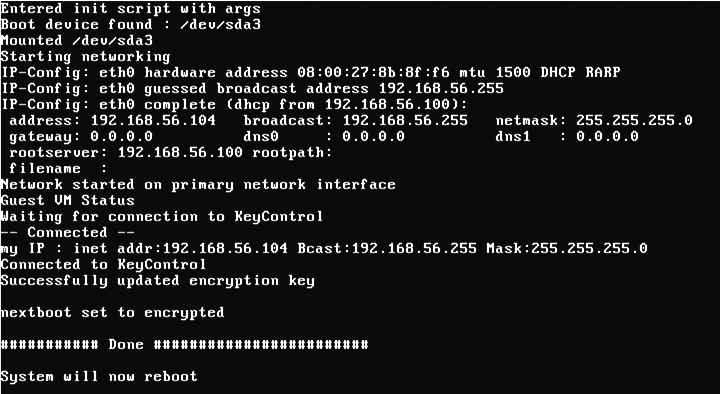
The Bootloader uses a small pre-boot environment to retrieve encryption keys for the boot device each time the system starts up. The system is reconfigured to boot the Bootloader before booting Windows. Here are the steps:
- A computer with has an encrypted boot drive reboots.
- The Bootloader intercepts the boot request and sends a request to Cryptographic Security Platform Vault to retrieve the encryption key for the
C:drive. - The Bootloader retrieves the key from Cryptographic Security Platform Vault and supplies it to the secondary boot stage, which will boot Windows.
- Windows boots normally.
Note: Keys for the C: drive are never stored persistently on the VM—they are only stored in the remote, password protected, Cryptographic Security Platform Vault object store. The following topics describe some of the possible outcomes in the boot process.
While the Bootloader is running, you can watch its progress through messages displayed on the Windows boot screen.